Taylor Farms lettuce has been linked to a cyclosporiasis outbreak, and while the brand is taking action, shoppers may want to know where its products are sold.

Mashed – Fast Food, Celebrity Chefs, Grocery, Reviews

Taylor Farms lettuce has been linked to a cyclosporiasis outbreak, and while the brand is taking action, shoppers may want to know where its products are sold.
Mashed – Fast Food, Celebrity Chefs, Grocery, Reviews

The Romans taught us many things, but they also mastered one way to beat the heat, all of which can be traced back to one refreshing, retro-coded beverage.

Food Republic – Restaurants, Reviews, Recipes, Cooking Tips
The 7.0.2 security release addresses one critical and one high severity security issue.
Because this is a security release, it is recommended that you update your sites immediately. Due to the severity, the WordPress.org team have enabled forced updates via the auto-update system for sites running affected versions.
To manually update you can visit your WordPress Dashboard, click “Updates”, and then click “Update Now”, or you can download WordPress 7.0.2 from WordPress.org. On sites that support automatic background updates, the update process will begin automatically.
The security team would like to thank the following people for responsibly reporting vulnerabilities and allowing them to be fixed in this release:
For more information on this release, please visit the HelpHub site.
This release was led by John Blackbourn and Barry Abrahamson. In addition to the security researchers mentioned above, WordPress 7.0.2 would not have been possible without the significant contributions of the following people: Aaron Jorbin, Alex Concha, annezazu, Barry, David Baumwald, Dominik Schilling, Ehtisham Siddiqui, Joe Dolson, Joe Hoyle, John Blackbourn, Jonathan Desrosiers, Marius L. J., Matt Mullenweg, Mohammad Jangda, Peter Wilson, Sergey Biryukov, vortfu, Weston Ruter, plus representatives from Altis, Automattic, Bluehost, Cloudflare, GoDaddy, Hostinger, and WP Engine.
WordPress Planet

There are now four concerts on Garth Brooks’ 2026 tour itinerary. The singer and songwriter just announced two additional Blame It All On My Roots Tour dates.
Garth Brooks announced his 2026 Blame It All On My Roots Tour on July 7.
It begins in Indianapolis, Ind., wi
…
Read More
… Continue reading…Country Music News – Taste of Country
There are now four concerts on Garth Brooks’ 2026 tour itinerary. The singer and songwriter just announced two additional Blame It All On My Roots Tour dates.
Garth Brooks announced his 2026 Blame It All On My Roots Tour on July 7.
It begins in Indianapolis, Ind., wi
…
Read More
… Continue reading…The Boot – Country Music News, Music Videos and Songs
The warehouse giant relies upon a place that has a focus on sustainable farming, humane treatment of animals, and responsible land stewardship.
Mashed – Fast Food, Celebrity Chefs, Grocery, Reviews

Hank Williams Jr. has been forced to postpone two concerts originally scheduled for this weekend due to poor air quality conditions across Michigan.
The Great Lakes State has experienced some of the worst air quality in the United States this week as smoke from wildfires burning in Minnesota and parts of Canada has moved into the region, creating hazardous conditions for residents and visitors.
According to The Detroit News, the conditions across the state could be “very unhealthy and hazardous.”
Hank Jr.’s team announced the schedule changes on social media early Friday morning, revealing that both of his Michigan shows have been rescheduled for next month.
“Out of an abundance of caution regarding air quality, this weekend’s Hank Williams Jr. shows in Michigan have been postponed and rescheduled to August 13 at Pine Knob Music Theatre and August 14 at Acrisure Amphitheater,” the statement read.
The team also assured ticket holders that their tickets will remain valid for the new dates.
“All previously purchased tickets will be honored for the new dates. More information will be emailed directly to ticketholders,” they added.
Fans who were planning to attend the shows are encouraged to hold onto their tickets and await further updates from the venues and ticket providers.
Hank Williams Jr.’s concerts aren’t the only country music events being impacted by wildfire smoke across the Midwest.
Country Thunder Wisconsin, which kicked off Thursday and runs through Sunday, has been keeping attendees updated as officials continue to monitor air quality conditions caused by the wildfire smoke. The festival shared that it is working closely with local officials to ensure the safety of everyone on-site.
“Your health and safety is our top priority, and we will be providing masks for attendees at all entrance points if required,” the festival shared in its latest statement.
Organizers also reminded fans that “onsite medical staff is available 24/7 to assist with anyone experiencing health concerns.”
Meanwhile, Country Jam USA in Eau Claire, Wisconsin, is also moving forward as planned while keeping a close eye on conditions. Festival organizers said they are working with emergency coordination teams to monitor smoke alerts and the heat index throughout the event.
Fans attending the festival are encouraged to stay hydrated, take breaks in shaded areas, and wear masks if the smoke begins to impact them.
The post Wildfire Smoke Forces Hank Williams Jr. To Postpone Michigan Concerts, Impacts Midwest Festivals appeared first on Country Now.
Country Now
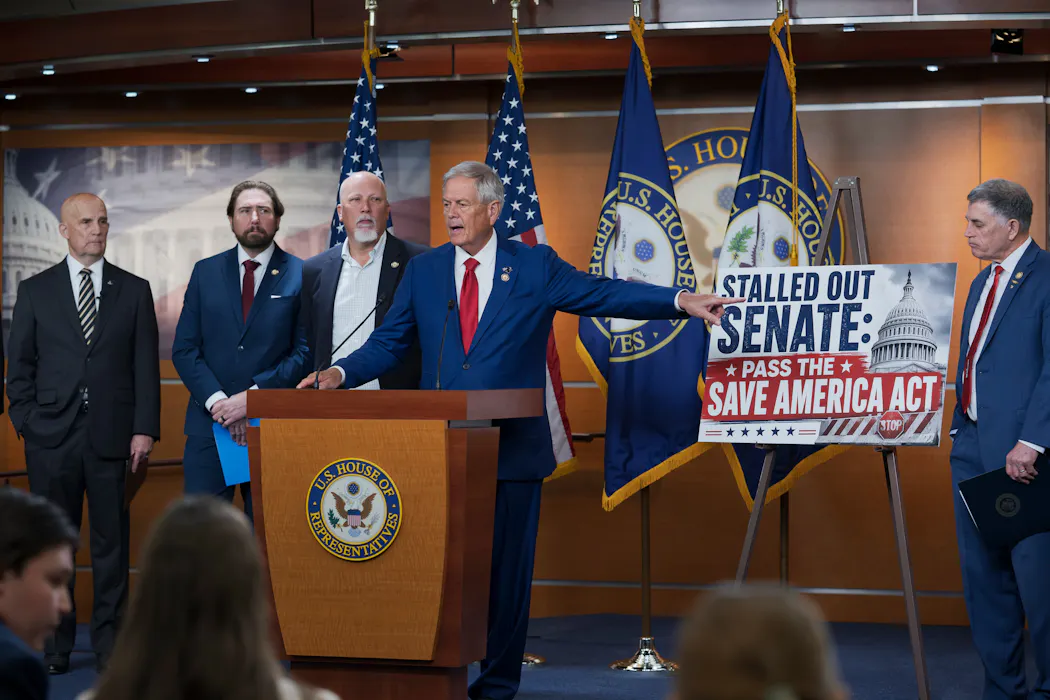
President Donald Trump’s obsession with unfounded claims of election fraud has defined his second term in office. But in recent months his fixation has moved from executive nominee litmus tests and executive orders reinforcing proof of citizenship to vote into legislation – dragging Congress into the fray.
The Safeguard American Voter Eligibility Act, or the SAVE America Act, featured heavily in Trump’s primetime speech on July 16, 2026.
It’s become the focus of the administration in recent months, eclipsing prior legislative efforts by proposing stringent and widespread voting changes. The proposed law, which would federalize elections, require additional documentation in order to vote and curtail mail-in registration and ballots in all states, faces major logistical, legal and political hurdles.
The act, which is stuck in limbo between the U.S. House and Senate, has dominated and derailed the summer’s legislative calendar. In the House, Republican members delayed votes on major legislation in an effort to pressure the Senate to take the bill up for a vote, and it has become a sticking point in other unrelated legislation.
The controversial act has also soured the relationship between Trump and members of his party, leading him to refuse to sign a bipartisan housing bill passed by Congress. Although the bill became law without his signature, Trump’s preoccupation with the SAVE America Act ultimately denied congressional Republicans an opportunity to tout a bipartisan, popular policy win.
Yet, despite mounting political pressure, Congress hasn’t budged.
This tension between Trump’s priorities and congressional inaction is noteworthy because Republicans control both chambers. But as a political scientist who studies the evolving power of congressional leadership, I find inaction on the SAVE America Act to be more than a reflection of Trump’s waning popularity among Republican lawmakers. Rather, congressional hesitation on what would be the largest election reform in decades reflects an awareness of constituent needs and lawmakers’ own reelection risks.
House Republicans have been quick to blame the Senate – and the 60-vote filibuster threshold the legislation must overcome to receive a vote on the Senate floor – for the inaction.
House Speaker Mike Johnson has brought the legislation to the floor for at least three votes in an effort to pressure the Senate to take up the legislation. In July 2026, Johnson took a more creative approach, relenting to conservative lawmakers by including portions of the SAVE America Act in a House-passed bill to fund the State Department.
These actions are largely theatrical. Senate Majority Leader John Thune has said since February 2026 that there aren’t enough votes to move the SAVE America Act through the Senate, telling Fox News in June that “the votes currently aren’t there.” Although Senate Republicans could vote to remove the filibuster, which Trump has also requested, they have not.
Even in the House, the slim margins of Republican control have made it challenging for Johnson to keep the party together on the controversial issue. And Johnson’s gambit to attach the SAVE America Act to important legislation risks not only derailing bipartisan policy but another government shutdown, too.
If Republicans were serious about electoral reform, including moderate reforms that the majority of Americans do support, their approach would be like that used for other major legislation: bipartisan. Instead, partisan passage of a controversial bill, with a known Senate blockade, presents half-hearted strategy that avoids true responsibility.
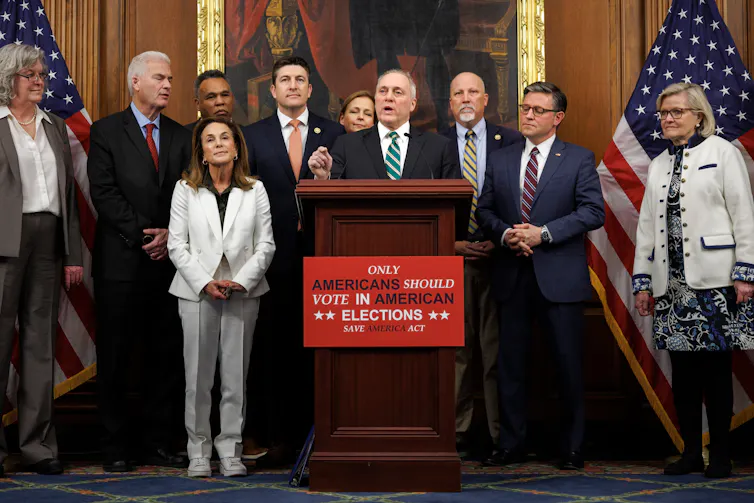
The SAVE America Act would be confusing, time-consuming and expensive, and it would not provide funding to help states implement changes.
Changing election processes warrants precision and time, too. As Republican Sen. Thom Tillis noted, “Do you honestly believe that we can have this thing up in 50 states? There’s no funding. There’s no specific implementation instructions.”
Beyond logistics, the legality of federalizing election processes is murky.
Congress does have the power to mandate election requirements. But under Article 1, Section 4, of the Constitution, while Congress can outline parameters, states are responsible for election administration.
For example, the National Voter Registration Act of 1993 reinforced citizenship as a requirement, but states maintained responsibility for creating their own form and enrollment process. The SAVE America Act attempts to circumvent this by requiring federal possession of voter rolls.
Beyond legal challenges, the SAVE America Act introduces very real implications for American voters – and the members of Congress who represent them.
While the act’s stated goal is to ensure only citizens vote, citizenship requirements for voting are already federal law. In practice, many scholars believe the bill would make it more difficult for eligible voters to engage in the democratic process.
For rural Americans, most of whom are represented by Republican members of Congress, the act would sharply restrict mail-in registration and mail-in voting. More than 5 million Americans would need to drive an hour or more to register to vote, with some voters facing drives as long as eight hours.
For women who changed their name after marriage, a trait more likely to be associated with Republican women, voting would require marriage certificates in addition to birth certificates.
First-time voters, young voters on college campuses and voters who have recently moved could also face the hurdle of finding and presenting this documentation in person.
Members of Congress, particularly those who represent rural areas, are likely aware of this reality. Disenfranchising or, at best, confusing their voters risks their own electoral success, too.
One of Trump’s first acts following the Supreme Court’s ruling in Trump v. Slaughter in June 2026, which allowed the president to remove executive branch officials without cause, was to fire the remaining members of the bipartisan, Senate-confirmed Election Assistance Commission.
The agency is the point of contact for states regarding election administration processes, offering resources, guidance and expertise on voting logistics. If the SAVE America Act were to pass, this office would be integral to ensuring changes are unbiased and fair across all 50 states.
Coupled with warnings that Trump may invoke emergency powers over election administration, aggressive actions by the Department of Justice to control voter rolls, partisan redistricting, and now a vacated election commission, the SAVE America Act risks further disrupting elections. All while these elections have already been secure and overwhelmingly free of fraud.
As Tillis noted to reporters, “They’re being disingenuous to suggest to the American people they could possibly be operational by this election. And so then it begins to make me wonder … if we’re just beginning to undermine the underlying integrity of any of our elections. And I think that’s dangerous, and I think it’s wrong.”
Does Congress’ hesitation to pass the SAVE America Act reflect a weakened Trump grip on the Republican party? Possibly. The president is more unpopular than he has been at any point during his second term. Ignoring Trump on the SAVE America Act may be a risk worth taking to some members.
But for most Republican members of Congress, appeasing Trump remains key to primary and electoral success. The president’s record on primary endorsements – even for Senate incumbents – remains strong, as he continues to define the party. Among constituents, some provisions of the SAVE America Act are popular among MAGA-aligned voters, making it an important electoral issue for members representing deep-red districts.
By publicly supporting the act, but relying on the Senate to serve as a doorstop to House-passed legislation, Congress falls into a familiar pattern that allows conservative members to appeal to the president while using procedure to block legislation that would make major changes to voting, mere months from Election Day.
Congress’ hesitance to pass the SAVE America Act is more than a test of its relationship with Trump. It’s an example of Congress doing what it was intended to do: represent its constituents.

SoRelle Wyckoff Gaynor does not work for, consult, own shares in or receive funding from any company or organization that would benefit from this article, and has disclosed no relevant affiliations beyond their academic appointment.
Politics + Society – The Conversation
With the cost of everything on the rise, getting a quick meal at an affordable price is becoming more of a necessity. Some restaurants offer great discounts.
Food Republic – Restaurants, Reviews, Recipes, Cooking Tips
If you run a WordPress site, then you know that spam is a real annoying problem whether it comes to contact forms, WordPress comments, or user registrations.
The good news is that stopping spam in WordPress is a lot easier than you probably think, and you don’t need expensive tools either.
We have spent over 16 years testing anti-spam plugins, tools, and refining strategies to keep WPBeginner and our other business websites safe from daily spam attacks.
In this ultimate guide, we’ll walk you through how to block each type of WordPress spam, step by step from the basics to advanced modern automated spam protection. These are the exact methods we’re using to protect our own websites.
We’re covering a lot of ground in this ultimate guide, so use the quick links below to jump straight to the section you want to learn about first:
WordPress comes with several anti-spam options that can protect your site against spam. These built-in options won’t stop every bot, but they will remove the easiest targets right away.
We always recommend turning these settings on first, because they cost nothing and take only a few minutes to set up.
To prevent comment spam, the built-in discussion settings in WordPress act as your first line of defense. They allow you to control who can post, what kind of links are permitted, and how much control you have over the conversation.
To configure these anti-spam controls, go to Settings » Discussion in your WordPress dashboard.
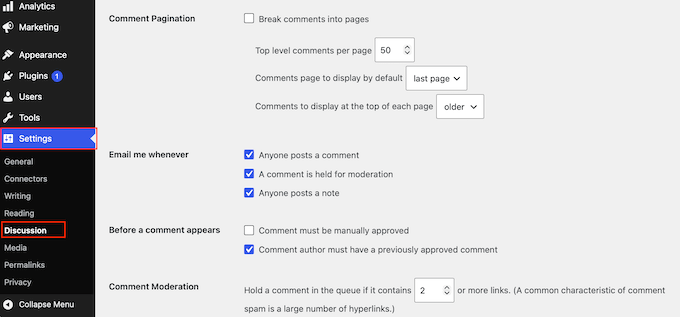
The most useful tool on this screen is the comment moderation queue. This tool acts as a holding area that keeps submissions hidden from the public until you have a chance to look them over.
Because nothing goes live automatically, spam never reaches your visitors, even if it manages to get past your other filters.
To turn this on, scroll down to the ‘Before a comment appears’ section and check the box next to ‘Comment must be manually approved.’
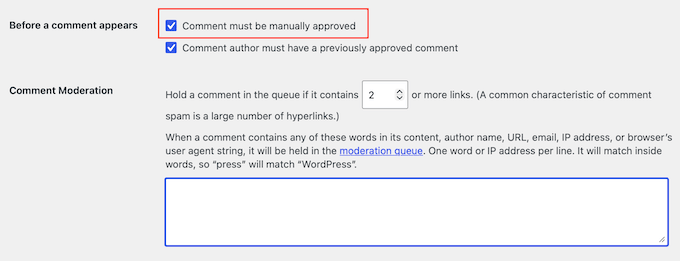
If you want, you can also enable ‘Comment author must have a previously approved comment.’ This lets returning commenters post without waiting for approval. However, be sure to review your published comments regularly since they won’t appear in your moderation queue.
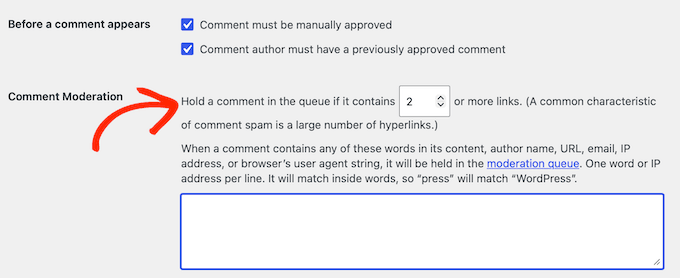
After that, scroll to the ‘Comment Moderation’ box, where you’ll find a setting that limits links. Because spam comments almost always contain web addresses, WordPress can automatically hold any submission that includes too many links.
The field labeled ‘Hold a comment in the queue if it contains [X] or more links’ is set to 2 by default. Lowering that number to 1 will help you catch even more junk.
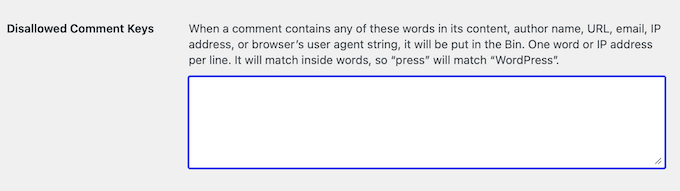
On the same screen, you can use the comment blocklist to automatically filter out unwanted content. This tool looks for specific words, names, email addresses, or web addresses and sends any matching comment straight to the trash.
In the ‘Disallowed Comment Keys’ box, you can paste your own trigger words, putting one on each line, and then save your changes.
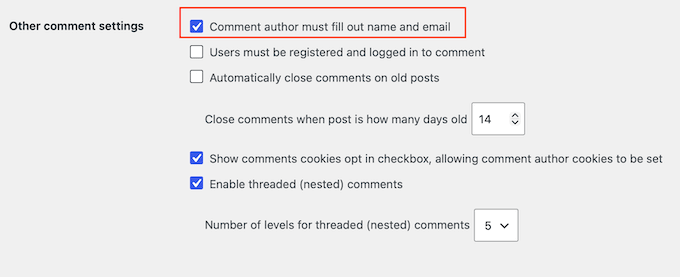
Healthy discussions start with real people. Requiring commenters to enter a name and email encourages more thoughtful conversations and discourages anonymous drive-by comments.
Most genuine visitors won’t mind providing these details, and it helps create a more welcoming and trustworthy community around your website.
To enable this, scroll to the ‘Other comment settings’ section and check the box next to ‘Comment author must fill out name and email.’
If you want to master the review process and manage your queue efficiently, our beginner’s guide to moderating comments in WordPress covers the full workflow.
Depending on the type of website you have, you may not need a comment section at all. If that’s the case, then you can simply disable comments entirely and that’ll get rid of the WordPress comment spam problem once and for all.
The most thorough option is the code method, which disables comment support across your entire site at once. It’s safest to add the snippet with a free code snippets plugin like WPCode rather than editing your theme’s files directly, so a theme update can’t undo it.
add_action('admin_init', function () {
    // Redirect any user trying to access comments page
    global $pagenow;

    if ($pagenow === 'edit-comments.php') {
        wp_safe_redirect(admin_url());
        exit;
    }

    // Remove comments metabox from dashboard
    remove_meta_box('dashboard_recent_comments', 'dashboard', 'normal');

    // Disable support for comments and trackbacks in post types
    foreach (get_post_types() as $post_type) {
        if (post_type_supports($post_type, 'comments')) {
            remove_post_type_support($post_type, 'comments');
            remove_post_type_support($post_type, 'trackbacks');
        }
    }
});

// Close comments on the front-end
add_filter('comments_open', '__return_false', 20, 2);
add_filter('pings_open', '__return_false', 20, 2);

// Hide existing comments
add_filter('comments_array', '__return_empty_array', 10, 2);

// Remove comments page in menu
add_action('admin_menu', function () {
    remove_menu_page('edit-comments.php');
});

// Remove comments links from admin bar
add_action('init', function () {
    if (is_admin_bar_showing()) {
        remove_action('admin_bar_menu', 'wp_admin_bar_comments_menu', 60);
    }
});
Our guide on how to completely disable comments in WordPress walks through that snippet along with the other options.
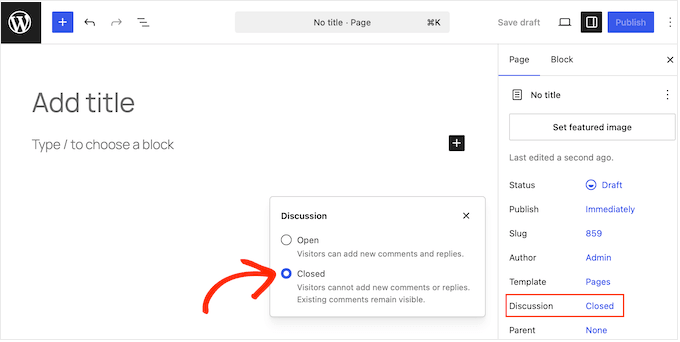
If you’d rather not go site-wide, you can also turn comments off on individual pages. This is handy when you only want them gone on specific pages, like your Contact or About pages, which rarely need a comment section.
To do this, open the page in the WordPress content editor. Then click the ‘Discussion’ option in the right-hand sidebar and select ‘Closed.’
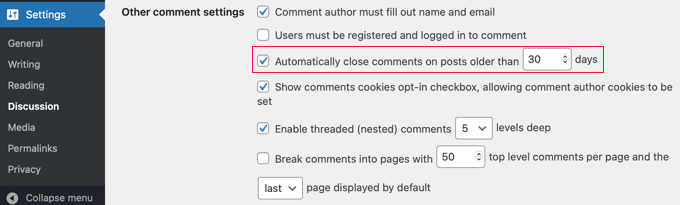
You can also stop spam from piling up on older content without touching your newer posts. If you don’t expect comments on old posts, then WordPress can close them automatically after a set number of days.
This gives spam bots fewer chances to target your archived content.
To set this up, head to Settings » Discussion and find the ‘Other comment settings’ section. Check the box next to ‘Automatically close comments on posts older than [X] days’, then set a sensible limit such as 30 or 90 days.
Trackbacks and pingbacks notify you when another website claims to have linked to one of your blog posts.
While they were originally designed to help bloggers connect conversations across different websites, they’re now commonly abused by spammers to send fake link notifications.
Turning this feature off completely removes a whole category of junk notifications from your dashboard.
To disable these notifications, go to the Settings » Discussion screen in your WordPress dashboard. Here, uncheck the box next to ‘Allow link notifications from other blogs (pingbacks and trackbacks) on new posts.’
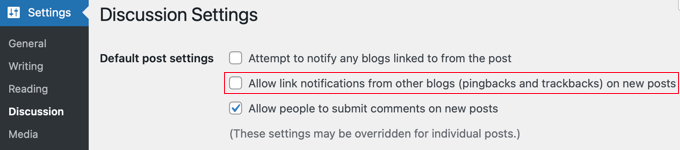
Just be aware that changing this option only protects the posts you publish from this moment forward. If you want to clean up the content you’ve already published in the past, you can follow our step-by-step guide on how to disable trackbacks and pings on existing WordPress posts.
In the era of AI where automated spam is increasing, the best defense against it is a modern AI-powered spam protection for WordPress.
These spam filtering solutions automatically detect and block spam on your WordPress comments, contact forms, and user registrations without the use of CAPTCHA which can hurt conversions.
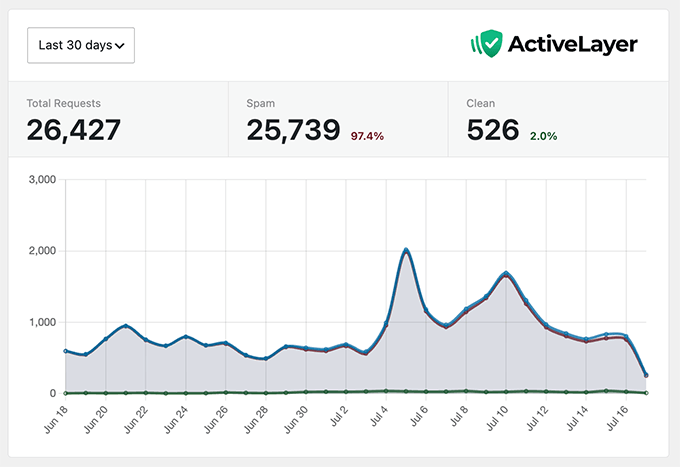
On WPBeginner, we use ActiveLayer for this. It is AI-powered and runs server-side, so it stops spam invisibly, without a CAPTCHA and it’s GDPR compliant.
In the last 30 days, it has blocked over 25,739 spam comments and contact form submissions on our website. It even shows you a confidence score, and the reason behind every submission it flags, not just a pass-or-fail verdict when you look at their logs.
The free plan includes 1,000 spam checks with no credit card, and paid plans start at around $4 per month billed yearly.
The two other popular spam filtering plugins for WordPress you could try are Akismet or CleanTalk.
Akismet is very popular and still is a good fit for personal blogs, where its “name your price” plan can be free for non-commercial sites. But they have raised their prices significantly for commercial sites which is quite expensive for smaller businesses. For a business site, we would point you to either ActiveLayer or CleanTalk.
Whichever tool you choose, stick to just one, because running two spam filters at once can conflict and block real visitors. The benefit of these spam protection plugins are that they integrate with all other popular contact form plugins by default.
So far we’ve configured the built-in spam prevention settings in WordPress, and an automated spam filtering plugin for WordPress. The combination of these two should block most spam.
However if you are not able to set up modern AI spam protection due to costs or another reason, then you can use one of these tips below to combat comment spam in WordPress.
CAPTCHA is a simple test that most human visitors pass without any effort, while automated scripts fail it. We recommend adding Cloudflare Turnstile CAPTCHA to your WordPress comments because it’s free and fairly straight forward to set up.
To set it up, install and activate the free Simple Cloudflare Turnstile plugin. You will be asked to create a free account on Cloudflare’s website and connect it with the plugin.
Once that’s done, you can scroll to the ‘Enable Turnstile on your forms’ section. Simply check the boxes to protect all your WordPress forms and click ‘Save Changes’.
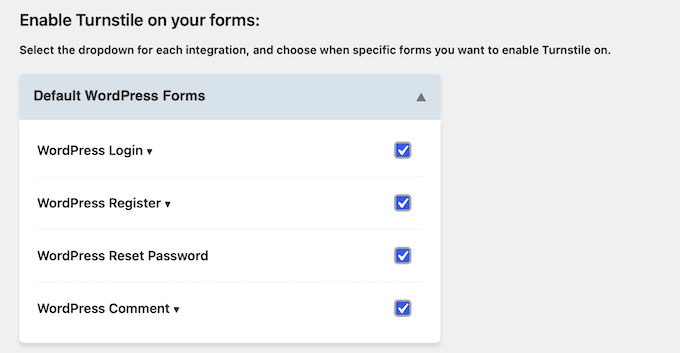
Here’s our detailed guide on how to add Cloudflare Turnstile CAPTCHA in WordPress.
Google reCAPTCHA is another option, which you can add with the Advanced Google reCAPTCHA plugin. We no longer recommend it because Google has capped their free tier at 10,000 assessments per month for your entire organization whereas Cloudflare Turnstile stay free without limits.
Another really effective way to stop comment spam in WordPress is to control who’s allowed to participate in comments.
If your comment section is open to everyone, then spammers can continuously flood your forms with automated links. Restricting comments to registered account holders ensures that only verified users can post. This forces a level of accountability that most bots will not bother trying to bypass.
Because it requires readers to go through the extra step of creating and logging into an account, this approach is best suited for membership sites, online forums, and private communities.
If you run an open, public blog, then we’d recommend using an automated filtering service or a reader challenge instead as those add less friction.
If you do decide to turn this restriction on, go to Settings » Discussion in your WordPress dashboard. Under the ‘Other comment settings’ section, check the box next to ‘Users must be registered and logged in to comment.’
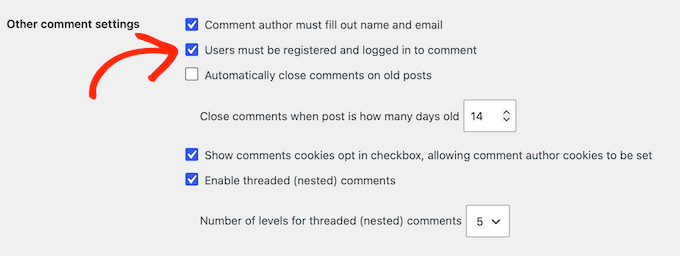
As always, don’t forget to save your changes.
Some spam slips through basic checks by mimicking human writing. This is where a dedicated filtering plugin can help protect your site.
Antispam Bee is an excellent free, privacy-friendly anti-spam plugin that doesn’t require an API key or account registration. Installing Antispam Bee gives you a powerful set of local rules to analyze comment data before it even hits your database.
Once it’s activated, you can configure your rules by going to Settings » Antispam Bee.
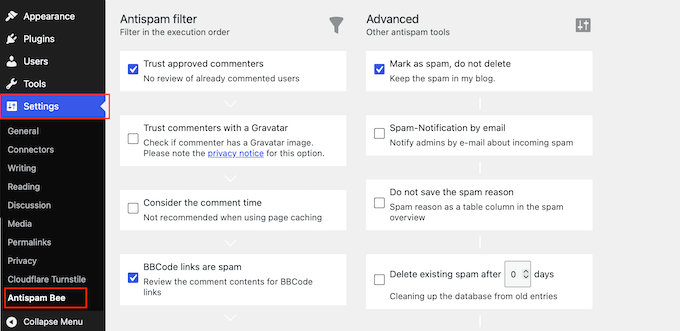
We recommend enabling the options to:
You should also check the box to ‘Look in the local spam database.’ This allows Antispam Bee to cross-reference new submissions against previous spam history on your site.
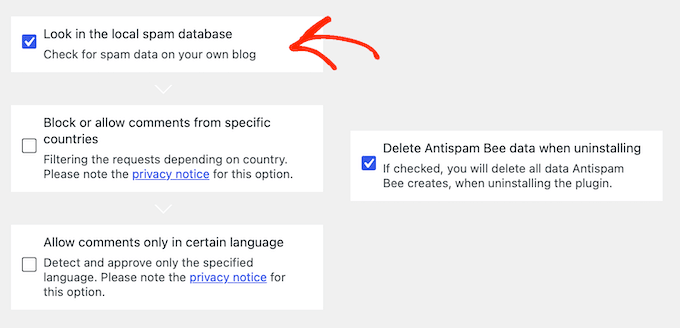
Under ‘Advanced,’ you can set Antispam Bee to delete existing spam after a set number of days, which keeps your database tidy without any manual effort.
We highly recommend leaving the email notifications for spam turned off in this section. A busy website can attract hundreds of automated submissions a day, and these alerts will quickly flood your inbox.
If you want to try one more free tweak, then you can remove the website address field from the comment form.
Our step-by-step guide on how to remove the website URL field from the comment form shows you how to do this in just a few quick steps.
Contact and lead forms are among the most attacked parts of any WordPress site. We know this firsthand because we once had to combat more than 18,000 spam entries flooding a single form.
We use WPForms to build forms on WPBeginner, and it’s a popular form builder plugin used by over 5 million websites. Their free version includes smart anti-spam protection, CAPTCHA integrations with Google / Cloudflare Turnstile, and the paid plans add the filtering options we cover below.
Other popular form builders like Gravity Forms and Fluent Forms have similar anti-spam settings, so check the options in whichever form builder plugin you use. We will show WPForms here because it’s what we use and consider the best fit for beginners.
To combat lead form spam, WPForms silently attaches a unique, time-sensitive token to your form on every page load. The anti-spam token blocks automated scripts, which means spam entries are blocked before they reach your inbox.
It’s turned on by default for new forms, but it’s worth confirming.
Open your form, go to Settings » Spam Protection and Security, and make sure ‘Enable modern anti-spam protection’ is switched on.
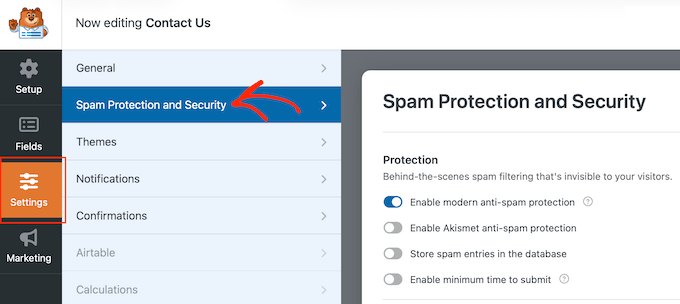
This is a modern version of the Honeypot technology which most WordPress form plugins come with, so it may be labeled as Honeypot in another form tool that you might be using.
More aggressive bots mimic human browsing and slip past the invisible token. Adding a visible CAPTCHA field stops them by forcing a challenge they can’t read or solve.
WPForms has both Cloudflare Turnstile and Google reCAPTCHA built in, and we default to Turnstile here. It’s free for everyone and runs its checks in the background, so most real visitors pass without solving a puzzle.
To set it up, go to WPForms » Settings » CAPTCHA and choose ‘Cloudflare Turnstile’.
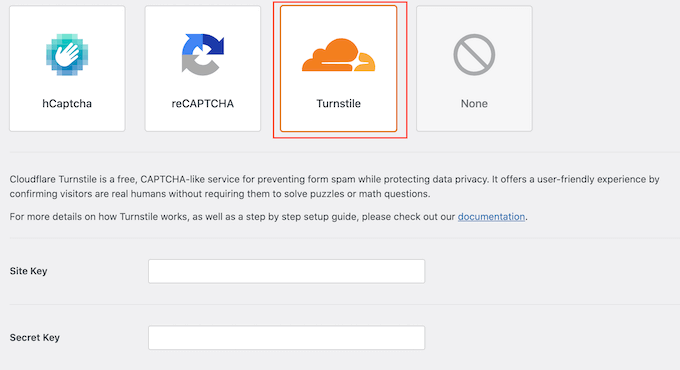
Then add the Site Key and Secret Key from your Cloudflare account, and save your settings.
Finally, add the CAPTCHA field to each form you want to protect.
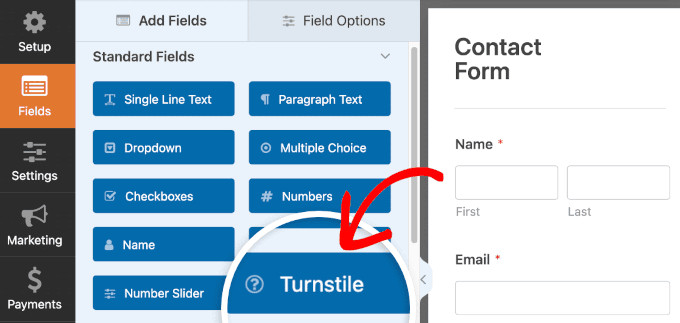
For a full walkthrough, see our guide on how to add Cloudflare Turnstile CAPTCHA in WordPress.
Google reCAPTCHA is also selectable on that same WPForms » Settings » CAPTCHA screen. We default to Turnstile because it’s free without limits, but reCAPTCHA still works if you prefer it.
If you’d rather not send visitor data to Google or Cloudflare, then WPForms’ Custom Captcha field (available on any paid plan) builds the challenge on your own server instead.
Add the field, then set it to a random math problem or your own question and answer.
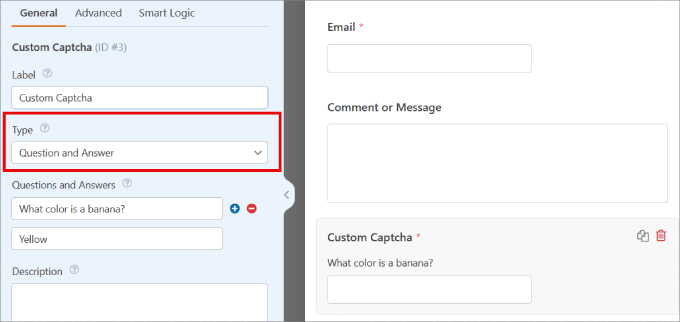
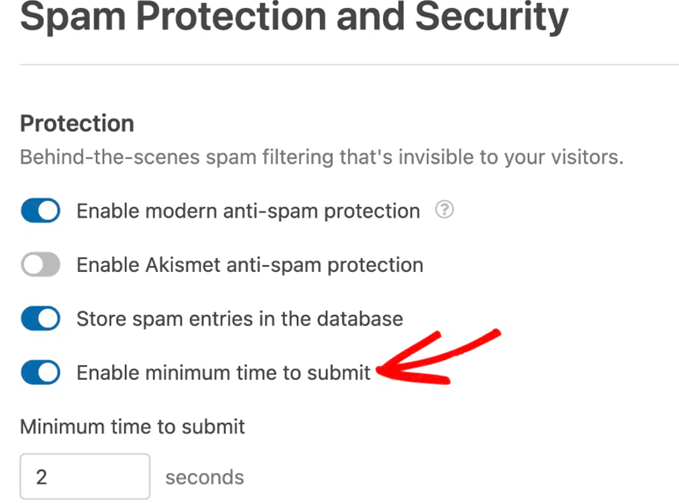
A real person needs several seconds to read a question and fill out a form, while a bot submits in a fraction of a second. Time-based checks flag those impossibly fast submissions without changing anything the visitor sees.
With WPForms, the ‘Enable minimum time to submit’ option is enabled by default with a minimum time to submit of 2 seconds. However, you can update the minimum time to any value you like.
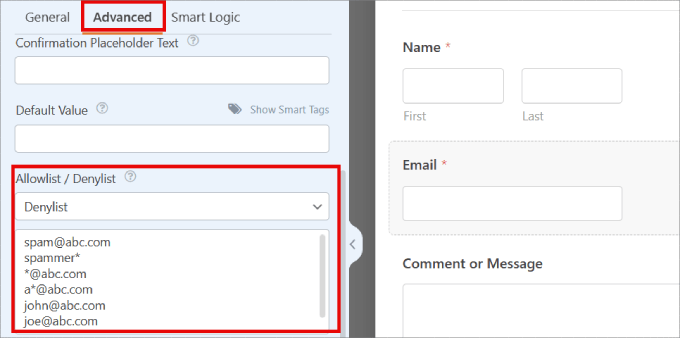
Some spam form submissions still gets through unless you screen the content itself. In the Pro version, WPForms lets you block entries by specific email address, by keyword, and by country or IP address.
To block a sender, open your form, select the Email field, open the Advanced tab, choose Denylist, and enter the addresses or domains to ban. A wildcard like *@example.com blocks an entire domain.
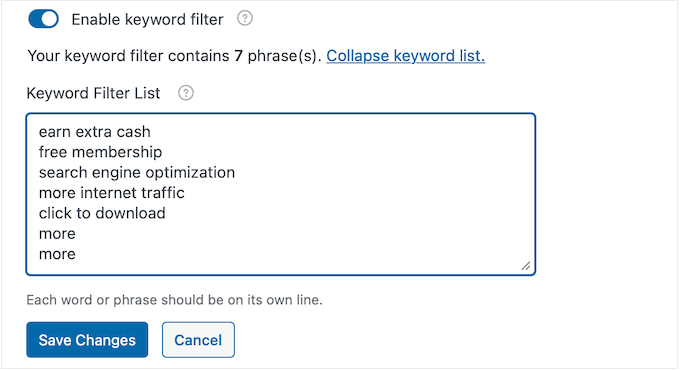
To block spammy phrases, go to Settings » Spam Protection and Security.
Turn on ‘Enable keyword filter’, open ‘Edit keyword list’, and add each term on its own line.
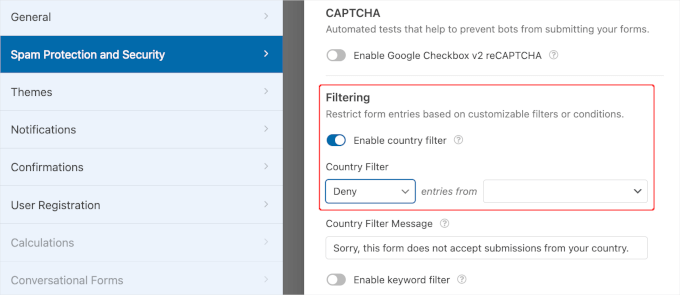
And if you only serve certain regions, turn on ‘Enable country filter’ on the same screen to allow or deny locations.
Alternatively if your WordPress form solution doesn’t have this option, you can also block IP addresses in WordPress.
On a membership site or WooCommerce store, spam registrations are more than a nuisance. Fake accounts clog your user database and skew your customer and email metrics.
Here’s what you can do to prevent spam user registrations in WordPress.
If you’re not running a membership site or an eCommerce store, then you likely don’t need to allow user registration. The easiest thing to prevent user registration spam there is to turn it off.
Simply go to Settings » General in your WordPress admin area, and uncheck the ‘Anyone can register’ box.
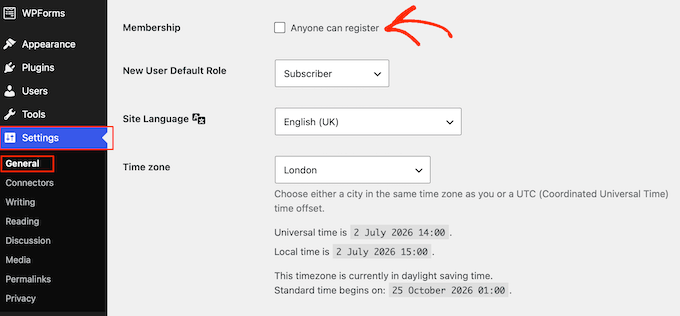
If you do need open registration, then the goal is to let only real people in while keeping spam bots out. The setting that stops the most fake signups is requiring a confirmed email address, or a manual review, before an account goes live.
Where that control lives depends on what plugin you’re using to manage user registration in WordPress. You will want to start with your platform’s default setting instead of bolting a general form plugin onto a system that already handles this.
If you run a WooCommerce store, then go to WooCommerce » Settings » Accounts & Privacy. This is where you decide whether shoppers can create an account at all, limit account creation to checkout, or keep guest checkout on so no account creation is needed.
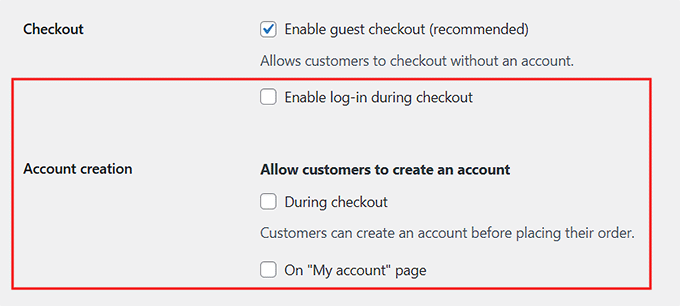
WooCommerce core doesn’t add a separate email-confirmation step on its own. If you want one, then you’ll need a custom email verification extension or the custom signup form covered below.
Other membership and course platforms handle account verification in their own settings, so start there:
If you’re building a custom registration form rather than using one of the systems above, then you can use WPForms User Registration addon which lets you turn on email activation under the form’s User Registration settings, with either an email confirmation link or manual admin approval.
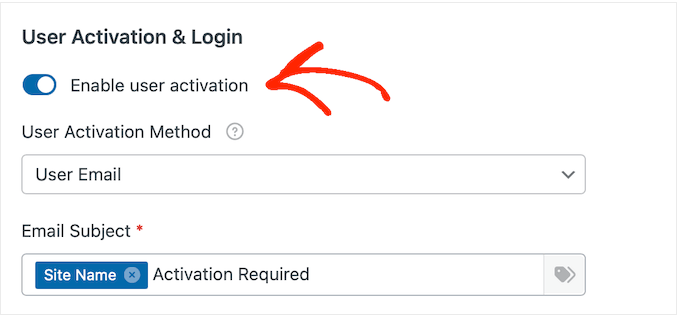
Similar options are available in Gravity Forms, WSForm, and other popular WordPress form plugins. For the full walkthrough, see our guide on how to moderate new user registrations.
The same tips that protect your WordPress contact forms also work on WordPress signup form. Since you already set up Cloudflare Turnstile earlier, you can switch it on for your registration form in a click.
For a dedicated walkthrough, see our guide on how to add a CAPTCHA to your login and registration forms.
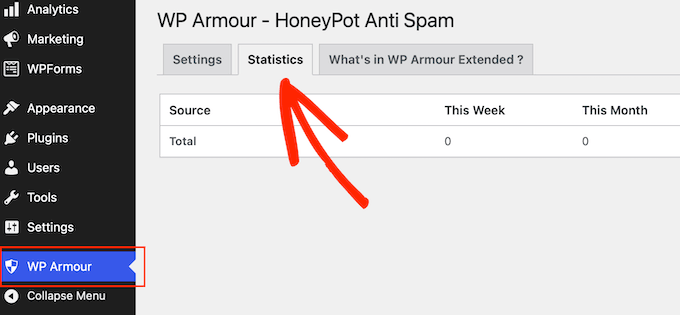
If you’re using the default WordPress registration page, then you can add hidden honeypot fields to your registration form with the free WP Armour plugin. The plugin logs every bot it blocks under WP Armour » Statistics.
Honeypots and CAPTCHAs stop obvious bots, but they can’t spot someone signing up with a throwaway email or from a known-bad IP address.
That’s where automated detection helps. It screens each new signup against live reputation data and blocks the ones that look fraudulent.
ActiveLayer and CleanTalk both offer this for WordPress registrations, and you can switch it on for your signup form the same way you did for your contact forms.
A Web Application Firewall (WAF) screens every visitor and blocks malicious requests before they reach your site. Since most form spam is automated, a good firewall can stop a lot of it at the perimeter.
We recommend a DNS-level firewall, which filters traffic on the provider’s network before it touches your server.
On WPBeginner, we use Cloudflare, which has a free plan with basic firewall protection (setup requires pointing your domain’s nameservers to Cloudflare).
Our guide on how to set up the free Cloudflare CDN and firewall walks through it.
Plus, our roundup of the best WordPress firewall plugins compares the other options if you want to weigh them up.
Stopping new spam is only half the job. If you’re like most websites, you already have a backlog of old junk that needs cleaning up.
A quick cleanup keeps your database tidy and helps your new tools run at their best.
🚨 Always create a complete WordPress backup before deleting anything in bulk. These actions permanently wipe data, with no undo button if you make a mistake.
WordPress spam filter flags junk comments but doesn’t delete them, so they can build up in your spam folder and take up database space until you clear them out.
In your dashboard, go to Comments, click the ‘Spam’ filter at the top, and hit ‘Empty Spam’ to permanently clear everything your filters caught.
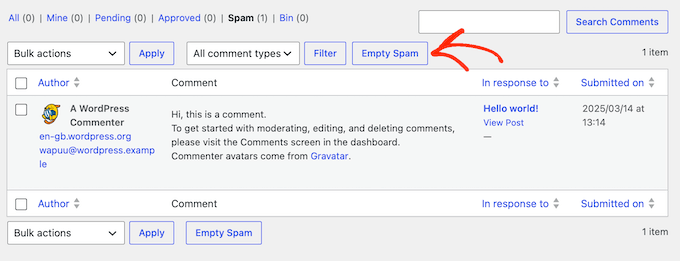
If you have thousands of junk comments, the dashboard can freeze or time out. A free plugin like WP Bulk Delete is faster and more reliable for big backlogs.
For other methods, see our guide on how to bulk delete WordPress comments.
Leaving bot profiles in your database is a security risk and skews your analytics. That’s why it’s important to clean out these fake accounts.
For a handful, go to Users » All Users, click the ‘Subscriber’ user role filter (the role almost all registration bots use), select the fake accounts, and choose Delete from the ‘Bulk actions’ menu.
⚠️ Be very careful to select only fake Subscriber accounts, and never an Administrator account.
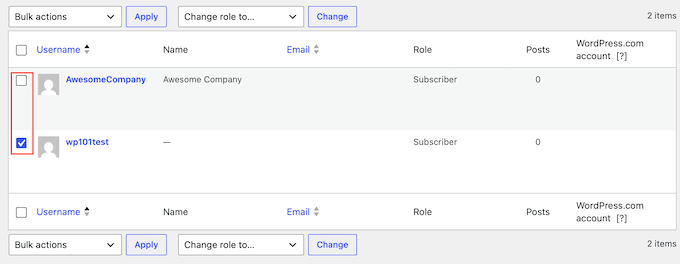
For thousands of accounts, the free WP Bulk Delete plugin can remove users by role, inactivity, or registration date in one sweep.
For more information, see our guide on how to bulk delete WordPress users by role.
No filter is perfect, so never auto-delete your spam folder without a quick glance first.
In Comments » Spam, hover over a legitimate comment and click ‘Not Spam’. That also teaches your filter to recognize similar comments as safe in the future.
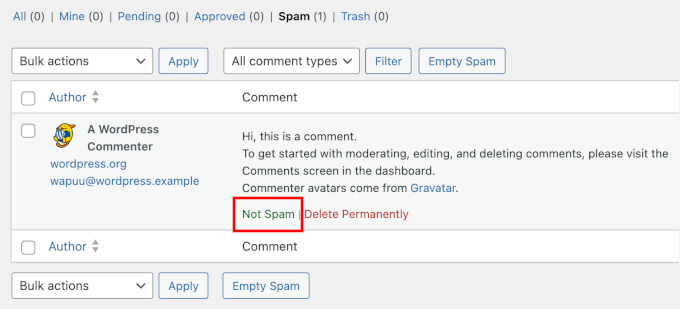
A few minutes each month keeps spam from piling back up. Add these three checks to your maintenance routine:
Here is a summary of the best practices we have covered to completely protect your WordPress website from spam:
Is free Akismet-style filtering enough, or do I need
more?
For a small personal blog with only comment spam, a single free filter like Akismet is usually enough. Once you add contact forms, signup forms, or user registration, you’ll want a service that protects those too, like ActiveLayer or CleanTalk.
Will adding a CAPTCHA hurt my form conversions?
It can. The extra step causes some real visitors to give up on the form. This is why we prefer invisible, server-side detection that blocks bots without asking anyone to solve a puzzle.
Why am I still getting spam after installing an anti-spam
plugin?
Usually because the plugin only guards one entry point. If it protects your
comments but not your signup or contact forms, bots just move to those
instead, and older tricks like basic honeypots no longer stop modern bots. The
fix is a layered setup: your built-in WordPress settings, an automated
filter, and a firewall working together.
How do I stop fake user registrations without turning off signups
completely?
Turn on email confirmation so new accounts stay inactive until the person
clicks a link in their inbox, which bots can’t do. Pair it with a honeypot and
an automated filter, and real people can still sign up freely.
Can spam actually hurt my SEO or get my site
blacklisted?
It can, but it depends on where the spam is. Comment spam sitting in your moderation queue is never published, so search engines never see it and your SEO stays safe.
Published spam is the real risk, because it can slowly pull down your rankings. WordPress does tag comment links as nofollow, which limits the damage.
We hope this article helped you learn how to protect your WordPress website against spam. You may also want to check out our ultimate WordPress security guide to improve your website security.
If you liked this article, then please subscribe to our YouTube Channel for WordPress video tutorials. You can also find us on Twitter and Facebook.
The post Ultimate WordPress Spam Protection Guide – Step by Step (2026) first appeared on WPBeginner.
WPBeginner